News

  • AI Supplier Questionnaire Analysis for Wheel Hub Procurement

    Freeze the questionnaire version, supplier identity, scope and original response before analysis. Define whether AI may classify completeness, summarize evidence, map answers to buyer requirements or suggest follow-up questions. Require citations back to the exact answer and attachment, label absent or ambiguous information instead of inferring it, and prohibit automatic supplier ratings or approvals. A qualified buyer, quality, technical, legal or security owner should verify consequential claims in their own domain, record exceptions and request clarifications. Preserve the prompt, model/service version, output, reviewer changes and final decision so later updates do not erase the audit trail.
  • AI Wheel Hub Warranty Triage: Human Review and Feedback Evidence

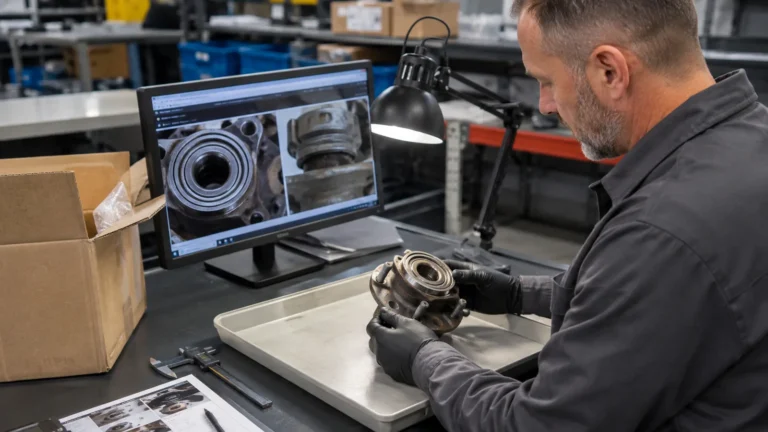
    Limit the system to a defined task such as routing, completeness checks, similarity search or priority suggestions. Preserve the claimant’s original text, images, installation and vehicle data, product and lot identity, timeline and prior handling. Test the tool on representative approved claims, including incomplete and conflicting cases, and review false escalation, missed severity and unequal treatment across channels. Present reasons and uncertainty to a qualified reviewer, who makes the disposition under the warranty terms. Separate feedback labels from unverified allegations, protect personal data, and provide a documented re-review route when new evidence arrives.

  • AI Wheel Hub Demand Forecasts: Override and Purchase-Decision Control

    Define the forecast level, horizon and decision it supports, then inventory the sales, stock, returns, supersession, promotion and external data used. Separate genuine demand from stockouts, one-time orders, channel transfers and catalog corrections. Evaluate forecasts by SKU group and decision cost, not only one average statistic. Present uncertainty and alternate scenarios to the planner, require documented overrides, and keep purchase-order approval independent from the model. Monitor bias, repeated stockouts, excess inventory and data drift; when a model or input changes, re-test affected segments and preserve a safe manual fallback.

  • AI Wheel Hub Image Classification: Validation and Exception Review

    Define whether the system is identifying product family, view angle, asset quality, possible mismatch or a different task. Build a labeled dataset from controlled wheel hub records, keeping duplicate shots and near-identical variants from leaking across training and acceptance sets. Include difficult lighting, packaging, occlusion, mirrored views, similar flanges and products with different encoder or spline details. Review false accepts and false rejects separately, require human escalation for uncertain or consequential cases, and bind release to the tested model, preprocessing and camera workflow. Never convert a visual label into fitment approval unless independent authoritative data confirms it.

  • AI-Generated Wheel Hub Catalog Copy: Source and Approval Control

    Start with an approved source packet for the exact SKU or product family, including controlled descriptions, dimensions, application data, packaging facts and claim restrictions. Tell the system to leave unsupported fields blank and prohibit invented fitment, torque, certification, material, warranty, origin, MOQ, lead time and capability statements. Preserve the prompt, source set and output version. A catalog reviewer should trace every factual sentence to a source, validate structured fields separately, inspect title and keyword use for clarity rather than stuffing, and approve channel-specific copy. When a fact changes, correct the authoritative record and every distributed version, not only the generated paragraph.

  • AI Wheel Hub Fitment Recommendations: Evaluation Before Catalog Release

    It must show performance on a representative, source-controlled test set that reflects the buyer’s actual catalogs, vehicle regions, years, positions and edge cases. Define the intended use and unacceptable outcomes before testing. Keep training, tuning and acceptance records separated where possible, label each expected result from authoritative application evidence, and measure false recommendations, missed valid options, unsupported answers and abstentions. Review consequential errors by category rather than relying on one average score. Release only the tested model, data and configuration; monitor live exceptions and retain a rollback path when the system or catalog changes.

  • AI-Assisted Wheel Hub Parts Identification: Human Verification Gate

    Treat the model output as a candidate list, not as an approved part number. Preserve the source photograph or measurement record, define what the tool was asked to do, and record the model or service version used. A qualified catalog reviewer should compare OE references, application records, dimensions, flange pattern, mounting position, drive configuration and encoder requirements against authoritative data. Reject low-quality inputs, contradictory evidence and candidates that cannot be separated by the available facts. Release a cross-reference only through the buyer’s normal approval route, with the source, reviewer, date, limitations and later correction path retained.

  • Wheel Hub Cybersecurity Contract Schedule: Evidence, Exceptions and Exit

    Identify the parties, services, systems, data classes and integrations covered, then assign responsibilities between buyer, supplier and service providers. Translate risk decisions into clear requirements for access, protection, logging, vulnerability and change communication, incident coordination, recovery, evidence and record retention. State how evidence is requested and protected, how exceptions are approved and time-bound, how subcontractors and material service changes are handled, and what happens at suspension or exit. NIST CSF 2.0 outcomes and informative references can help organize requirements, but they are not a certification clause and do not replace qualified legal review or jurisdiction-specific duties.

  • Wheel Hub Supplier Remote Support Access: Approval and Session Evidence

    Approve one support case before access begins, naming the affected system, task, data sensitivity, buyer owner and supplier technician. Use only an authorized remote-access method and a named identity with the minimum permissions and time window. Verify the technician through a trusted contact path, monitor or record the session according to policy, capture commands or changes at a useful level, and stop access if the scope expands. Afterward, test the intended result, review logs for unexpected activity, remove temporary software, accounts, tokens and sessions, and retain closure evidence. Never publish addresses, credentials, network topology or session recordings in an SEO article.

  • Wheel Hub Bank-Detail Change Verification Against Business Email Compromise

    Treat every payment-account change as high risk. Preserve the original request without using its links or contact details as the verification source, place the change and affected payment on hold, and contact the supplier through a previously approved independent channel. Require dual review across procurement or vendor management and finance, confirm the legal entity and beneficiary evidence, record what was verified and by whom, and allow the change only in the approved supplier-master workflow. Recheck the first payment under the organization’s policy and maintain an escalation route for conflicts. Cybersecurity guidance supports phishing awareness, MFA and incident reporting, but it does not replace banking, legal, sanctions or local payment requirements.

  • Wheel Hub Master Data Integrity: Approval, Detection and Recovery Evidence

    Identify the authoritative source for each critical field and preserve its revision, owner and evidence link. Route changes through a request that shows the prior value, proposed value, reason, affected SKUs and channels, reviewer and effective date. Use technical integrity signals such as file hashes, version control, database logs or reconciled exports where appropriate, but do not treat any one signal as proof that fitment or product content is correct. Monitor unusual or mass changes, investigate against source evidence, contain affected outputs, restore only a known-good state, and reconcile downstream catalogs and open transactions before release.

  • Wheel Hub Third-Party SaaS Register for Catalog and Order Data

    List each service that stores, transforms, transmits or authenticates catalog, fitment, quotation, order, payment-support or shipment data. Record the business owner, technical owner, provider, contracted entity, data classes, user and machine access, integrations, upstream and downstream dependencies, backup/export capability, monitoring, incident contact, renewal and exit requirements. Validate actual use rather than relying only on procurement records, and distinguish the provider’s responsibilities from the customer’s configuration duties. Review the register after integration, ownership, contract or service changes and before termination so data export, access removal and evidence retention are planned.

  • Wheel Hub Cyber Incident Notification and Order Continuity Playbook

    Define the events that require notification, the approved contacts on both sides, secure alternate channels, and the minimum first notice: detection time, affected service, known data or transactions, containment status and immediate buyer action. Preserve updates as facts change, distinguish confirmed impact from investigation, and keep legal or regulatory notification with the authorized owners. Activate a preapproved manual or alternate order path only after identity and duplicate-processing controls are confirmed. Recovery needs both security authorization and business reconciliation of catalogs, orders, acknowledgments, payments and shipments. NIST and CISA recommend integrating suppliers into incident response and recovery; they do not set one universal notice period for every commercial relationship.

  • Wheel Hub Catalog Backup and Restore Testing for Ransomware Readiness

    Inventory the catalog, fitment, product, price, order, shipment and supporting records that the business actually needs, then assign owners and recovery priority. Preserve protected backup copies under the organization’s security design and record when and how they were created without publishing storage details. Restore a selected recovery point into an isolated test environment, reconcile record counts and relationships, check known critical fields and transaction continuity, scan and authorize the environment before connection, and document gaps and remediation. CISA recommends offline encrypted backups and regular tests; NIST SP 1339 links backup management with change management and recovery exercises. Those sources guide the method, not a claim that a particular company is ransomware-proof.

  • Wheel Hub EDI and API Credentials: Rotation and Trading-Partner Control

    Register every credential by trading partner, environment, interface, endpoint, transaction scope, service owner and technical custodian. Exchange secrets through an approved secure method, never through ordinary article text, tickets or screenshots. Grant only the permissions needed, separate test and production, record issuance and rotation events, monitor authentication and unusual transaction patterns, and define immediate revocation and fallback procedures. Verification evidence may include identifiers, timestamps and outcomes, but the secret itself must not enter the audit report. A successful connection test proves only the tested transaction path and time window.

  • Wheel Hub Vendor Portal Access: Roles, MFA and Offboarding Control

    Create named accounts rather than shared identities, approve the minimum role needed for each user, and record the portal, organization, owner and data scope. Require an authentication method matched to risk and preserve evidence of configuration without storing secrets in the procurement file. CISA identifies phishing-resistant MFA as the strongest form of MFA, while NIST’s identity guidance treats authentication as a lifecycle that includes enrollment, recovery and revocation. Review privileged and inactive accounts, investigate anomalous access, and disable accounts promptly when employment, responsibility or the supplier relationship changes.